Hey there, it’s Jake, one of the co-founders at [Your Company Name], and lately, I’ve been getting a ton of messages from clients and potential partners panicking about desktop kiosk compliance. Like, I get it—regulations feel like moving goalposts, right? One minute you think you’ve nailed it, the next you’re hit with a reminder that kiosk data handling isn’t just “set it and forget it,” and accessibility rules aren’t just a nice-to-have. As a desktop kiosk supplier, this is literally my wheelhouse, but I know compliance can feel overwhelming if you’re not deep in the weeds like I am. So let’s cut the jargon, skip the formal lectures, and walk through how you can actually make sure your desktop kiosks check all the boxes—no fancy legal degree required. Desktop Kiosk

First off, let’s start with the basics you can’t skip: data privacy regulations. If your kiosk handles any kind of personal info—think name, email, credit card details, even just a user’s location—you’re not just operating, you’re playing by GDPR (if you’re in the EU), CCPA/CPRA (California, duh), HIPAA (if you’re in healthcare), or whatever regional rule applies to your users. Here’s the real tea from someone who’s seen this go sideways: I’ve had a client who ran a coffee shop kiosk that let users save their order preferences, and they forgot that meant they were storing personal data. That turned into a $1,200 fine from the California AG—not exactly the brand boost they wanted.
So how do you nail this? First, audit every single piece of data your kiosk collects. Are you grabbing a user’s full name just to say “Hey, [Name]”? That’s unnecessary—trim it to a first name only, or even skip it if you can. Then, make sure your data is stored securely. We don’t cut corners here at [Your Company Name]; every kiosk we sell has end-to-end encryption for data at rest and in transit. No plain-text credit card numbers, no unprotected user IDs. Also, build in easy opt-outs and data deletion—users should be able to wipe their kiosk session with one tap, no hoops to jump through. For HIPAA clients? We work with third-party auditors to make sure our kiosks meet all HIPAA’s security rule requirements, because handling patient info isn’t something to mess around with.
Next up, accessibility rules. This is the part a lot of businesses sleep on, and it’s not just about being nice—it’s legally required in a ton of places. In the US, that’s the ADA (Americans with Disabilities Act), and in other countries, it’s things like the UN Convention on the Rights of Persons with Disabilities. I’ve seen kiosks that have tiny text, no high-contrast mode, or no way for users with motor impairments to navigate without jabbing the screen super hard. That’s a problem. For example, a library client of ours got a complaint from a user with low vision because their kiosk’s text was only 12pt and didn’t have a zoom function. We retrofitted their kiosks with built-in screen zoom, high-contrast color schemes, and voice-over navigation—all standard on every desktop kiosk we offer now, by the way. Pro tip: test your kiosk with real users who have disabilities, not just your internal team. We work with local disability advocacy groups to beta-test our new kiosks, and it’s saved us from a lot of headaches down the line.
Then there’s payment card compliance, if your kiosk processes transactions. That’s PCI DSS, right? A lot of small businesses think “PCI only applies to big retailers,” but nope—if your kiosk swipes or takes credit cards, you need to be PCI compliant. We make sure every payment module we integrate into our desktop kiosks is PCI-approved, so our clients don’t have to go through the headache of getting their own approval on top of buying the kiosk. I’ll be honest, early on, we had a client who tried to use a cheap third-party payment module that wasn’t PCI-approved, and they got charged with non-compliance fees that were way more than the cost of upgrading to our modules. That’s a mistake we’ve made (learned from, obviously) so we build PCI compliance right in from day one for any kiosk that handles payments.
Wait, let’s not forget about physical safety. Desktop kiosks are usually on countertops, right? So they need to be stable—no tipping over if a user leans on it, especially if it’s in a busy spot like a mall or airport. We use weighted bases for all our desktop kiosks, and we test them for stability to meet OSHA (US) and ISO global safety standards. Also, if your kiosk has any sharp edges or hot parts (like a card reader that might get warm), we make sure those are covered so no one gets hurt. Simple stuff, but it’s part of compliance too.
Another big one: regional and industry-specific rules. This varies so much depending on where you’re deploying. For example, if you’re putting kiosks in a school, there are COPPA rules that restrict collecting data from kids under 13. If you’re in the financial services space, there are additional rules around fraud prevention and user verification. At [Your Company Name], we build our kiosks with modular features, so clients can toggle on or off compliance-specific tools based on their industry. Need COPPA compliance? We have a setting that blocks collecting any data from users under 13 and adds a parental consent prompt if needed. In finance? We integrate identity verification tools that meet FDIC requirements. It’s all about customization without adding extra work for our clients.
Now, here’s the part that’s easy to overlook: regular updates and audits. Compliance isn’t a one-time thing—regulations change, cyber threats evolve, and your kiosk software will get outdated if you don’t keep up. We have a team that pushes security and compliance updates to every kiosk we sell automatically, so our clients don’t have to remember to manually update their devices. Also, we recommend quarterly self-audits, and we even offer third-party audit services for clients who want an extra layer of peace of mind. I’ve had a client who thought they were compliant, but a quarterly audit found they’d stopped updating their kiosk software and had a small data leak—fixing that cost way less than a potential fine, so it’s worth doing.
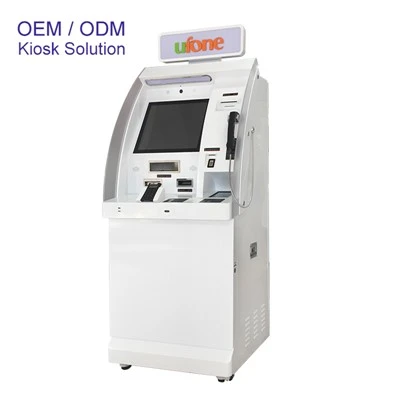
Let me be real with you: as a kiosk supplier, we’re not just selling a box with a screen. We’re selling compliance that actually works, without making our clients go through a million hoops. A lot of vendors will just sell you a kiosk and leave you to figure out compliance on your own, but that’s not how we operate. We’re here to help from the first design phase all the way through ongoing support. If you’re in the market for a desktop kiosk and don’t want to stress about missing compliance marks, hit us up. We can walk through your specific use case, answer all your questions, and make sure whatever kiosk we build for you checks every single regulatory box. No fine print, no confusing jargon, just real help.
SIM Card Dispenser Kiosk References:
- U.S. Access Board. (2023). ADA Standards for Accessible Design.
- European Data Protection Board. (2022). Guidelines on Data Processing in Digital Services.
- Payment Card Industry Security Standards Council. (2024). PCI DSS v4.0 Requirements.
- U.S. Department of Health and Human Services. (2023). HIPAA Security Rule.
- International Organization for Standardization. (2022). ISO 9241-171: Ergonomics of Human-System Interaction for Accessibility of Software and Services.
Hangzhou Smart Future Technology Co., Ltd.
As one of the most professional desktop kiosk manufacturers and suppliers in China, we’re featured by quality products and good service. Please rest assured to wholesale custom made desktop kiosk from our factory. Also, OEM&ODM service is available.
Address: China
E-mail: kelvin.kiosk@smartkiosktech.com
WebSite: https://www.smartkiosktech.com/
